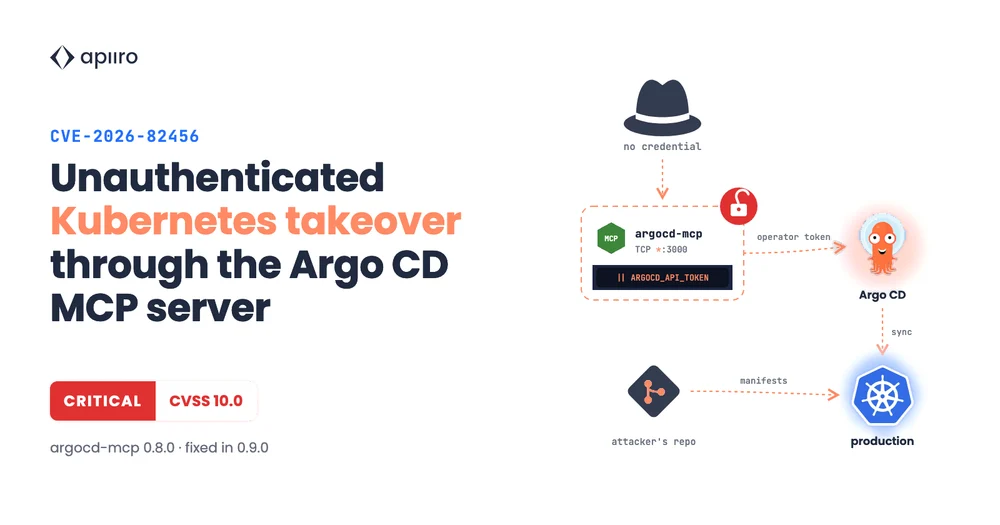
Argo CD MCP: unauthenticated cluster access
An investigation into the authentication boundary between an AI tool and the infrastructure it controls.
EnglishSecurity practitioners · Builders
Security / MCPTake a look
Security research
Published vulnerability disclosures and software supply-chain investigations, with links to the original evidence.
Three starting points
AI infrastructure, malware distribution, and an authentication bypass.
An investigation into the authentication boundary between an AI tool and the infrastructure it controls.
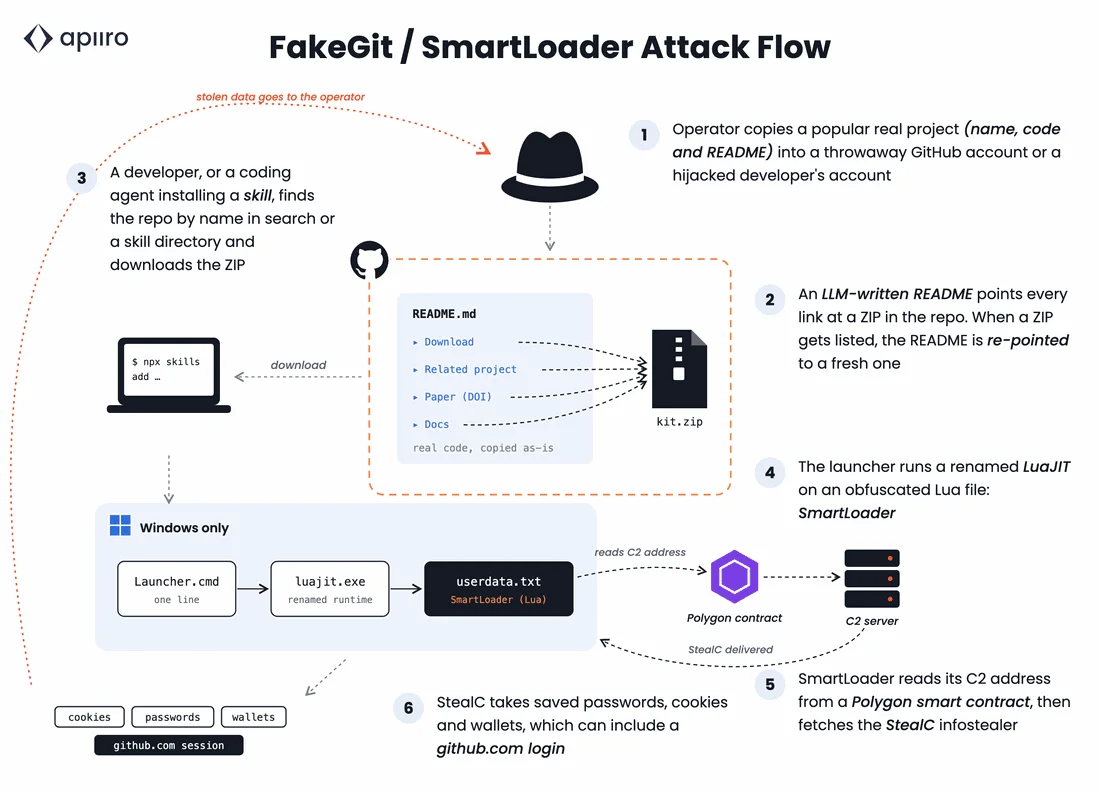
Following README link changes across the FakeGit software-supply-chain campaign.
CVE-2026-44338. Public maintainer advisory. Reporter credit may be shared with other researchers.
Campaigns & collaborative research
Original articles include the evidence, methods, and research-team credits.
Tracing npm dotenv look-alikes that concealed a PowerShell payload inside a JPEG.
Investigating a malware distribution network spread across GitHub and GitLab.
Collaborative research into vulnerabilities in open-source AI tools. The original article distinguishes each researcher’s findings.
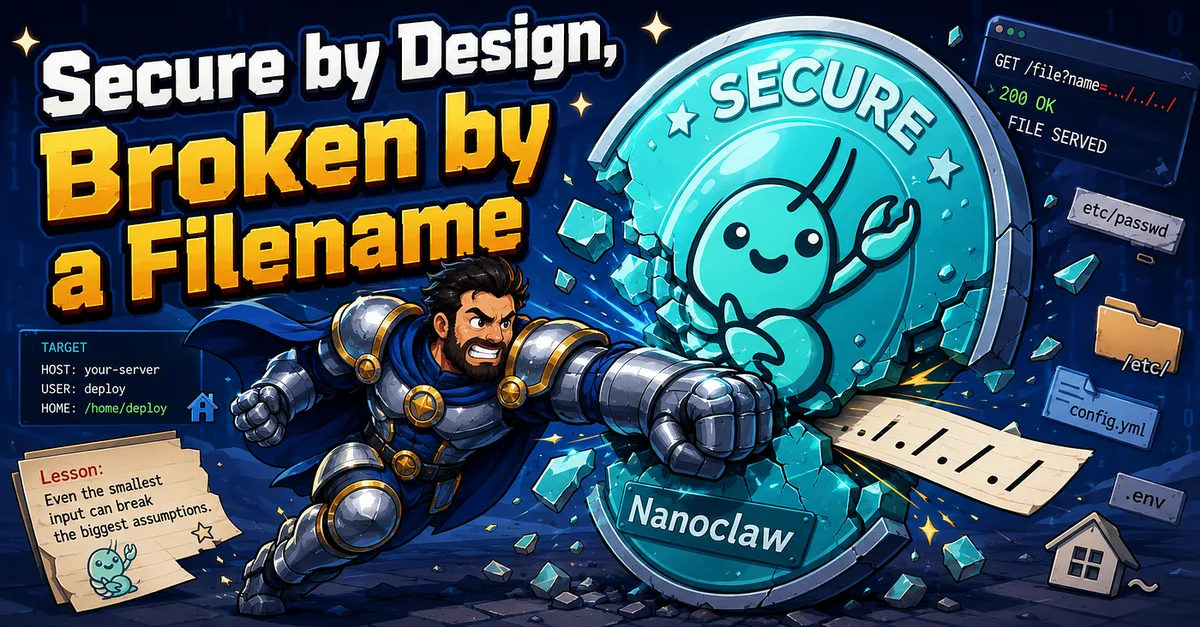
Two filename-validation gaps in host-side attachment handling: an inbound write and an outbound read. The public writeup links both maintainer fixes.
Maintainer advisories
Published findings with reporter credit. Consolidated advisories may include other researchers.
CVE-2026-118395. Missing scope enforcement on repository creation routes. Shared credit in the consolidated advisory.
Public maintainer advisory. Reporter credit may be shared with other researchers.
Authorization gaps in sales and order operations. The advisory narrative credits shmulc8 for the reported cases.
An unauthenticated signup path exposed a pending invitation token. Public advisory credits shmulc8.
CVE-2026-109527. Unbounded HTTP and OAuth body reads. Consolidated advisory with shared reporter credit.
An open redirect in the SAML login flow could expose a JWT to an external host. The public advisory credits my work account, shmulik-apiiro.
A malicious archive processed by the decompress plugin could escape the extraction directory and lead to code execution. The maintainer advisory credits shmulc8.
An unauthenticated arbitrary-file-read issue on Windows. Public advisory credits shmulc8.
CVE-2026-108395. Unbounded body reads in HTTP transports. Consolidated advisory with shared reporter credit.
CVE-2026-59257. Public maintainer advisory. Reporter credit may be shared with other researchers.
CVE-2026-47138. Public maintainer advisory. Reporter credit may be shared with other researchers.
CVE-2026-44337. Public maintainer advisory. Reporter credit may be shared with other researchers.
CVE-2026-44338. Public maintainer advisory. Reporter credit may be shared with other researchers.
CVE-2026-44339. Public maintainer advisory. Reporter credit may be shared with other researchers.
CVE-2026-42260. Public maintainer advisory. Reporter credit may be shared with other researchers.
CVE-2026-42312. Public maintainer advisory. Reporter credit may be shared with other researchers.
CVE-2026-42313. Public maintainer advisory. Reporter credit may be shared with other researchers.